Skip to content
Daniel TorresConnect

Senior Technical Program Manager · Cybersecurity, GRC and RMF

I lead complex technology programs.I engineer better ways to deliver.

15+ years leading cybersecurity, technology risk and transformation programs across federal and Fortune 100 environments.

PMP · CISM · Security+ · Network+ · A+

01Leadership and impact

Enterprise scale, mission outcomes.

The scope I carry today and the results behind fifteen years of program leadership.

High-High-High authorization programs owned, Step 1 through Step 6
3
High-High-High authorization programs owned, Step 1 through Step 6
U.S. Marine Corps
controls in each program, across IL5 and IL6 cloud
700+
controls in each program, across IL5 and IL6 cloud
U.S. Marine Corps
secured April 2026 for an operational hybrid cloud data center
ATO
secured April 2026 for an operational hybrid cloud data center
U.S. Marine Corps
controls in a Rev. 4 to Rev. 5 transition, 159 new or changed
702
controls in a Rev. 4 to Rev. 5 transition, 159 new or changed
In progress
mission owner systems in a rebuilt control inheritance model
13
mission owner systems in a rebuilt control inheritance model
U.S. Marine Corps
operational assets covered by RMF automation
1,400+
operational assets covered by RMF automation
Peraton Gold Award
fewer client compliance findings after a risk dashboard I built
38%
fewer client compliance findings after a risk dashboard I built
Fortune 100 consulting
ships reached by a PKI program I helped deliver
200+
ships reached by a PKI program I helped deliver
U.S. Navy, NAVWAR

02Programs I’ve led

Complex programs, organized, governed and delivered.

Each program below is told the same way: how I led it, what I built to execute it, and what it changed for the mission.

Featured program 01 · Security authorization

ATO secured April 2026 · continuous monitoring ongoing

Enterprise Security Authorization Program

Operational hybrid cloud data center · U.S. Marine Corps, MARFORCYBER / MCCOG

High-High-High programs
3
High-High-High programs
Controls per program
700+
Controls per program
Unclassified and classified cloud
IL5 + IL6
Unclassified and classified cloud
Full RMF lifecycle owned
Step 1 to 6
Full RMF lifecycle owned

Program leadership

Own the Risk Management Framework lifecycle end to end for three High-High-High programs. Serve as the working link between security managers, assessors, validators, engineering and the hardware and CMDB teams.

Technical execution

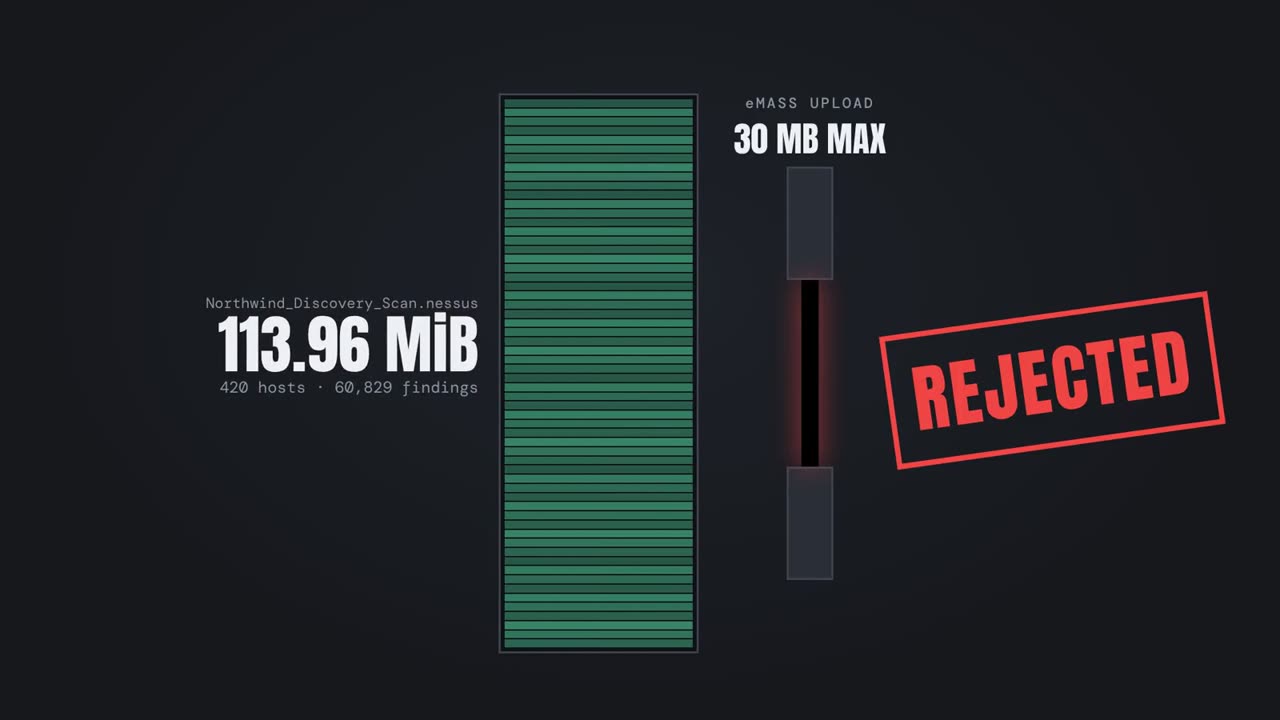
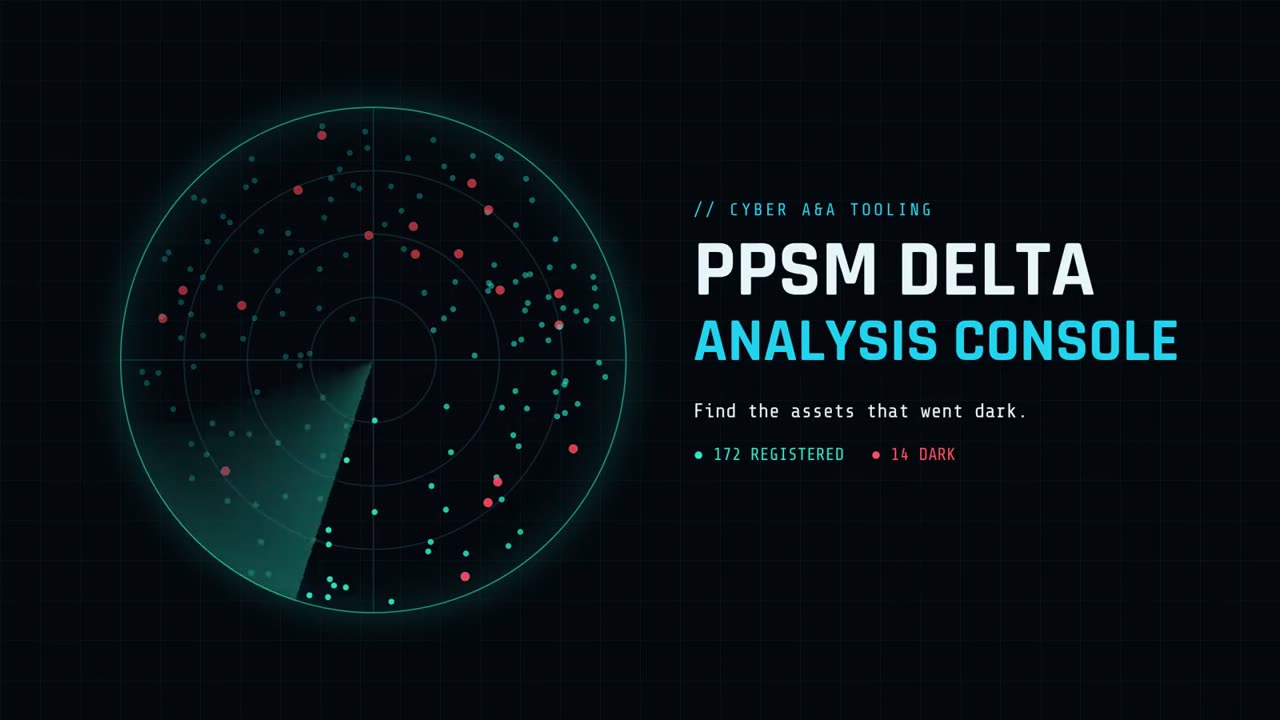
Built the tooling the program runs on: PARALLAX for package drift, RARE for risk assessment reports, Nessus Splitter for scan evidence and the PPSM console for network drift.

Mission value

Secured the data center’s Authorization to Operate in April 2026, and keep leadership current through weekly State of the Environment briefings.
Featured program 02 · Framework transformation

In progress · September 2027 target

Enterprise Cybersecurity Framework Modernization

NIST SP 800-53 Rev. 4 → Rev. 5 transition

Controls in scope
702
Controls in scope
New or changed controls
159
New or changed controls
Target completion year
2027
Target completion year
Governance cadence
Weekly
Governance cadence

Program leadership

Lead the transition roadmap toward a September 2027 target, with a weekly governance cadence that keeps engineering, operations and authorizing officials aligned on milestones and ownership.

Technical execution

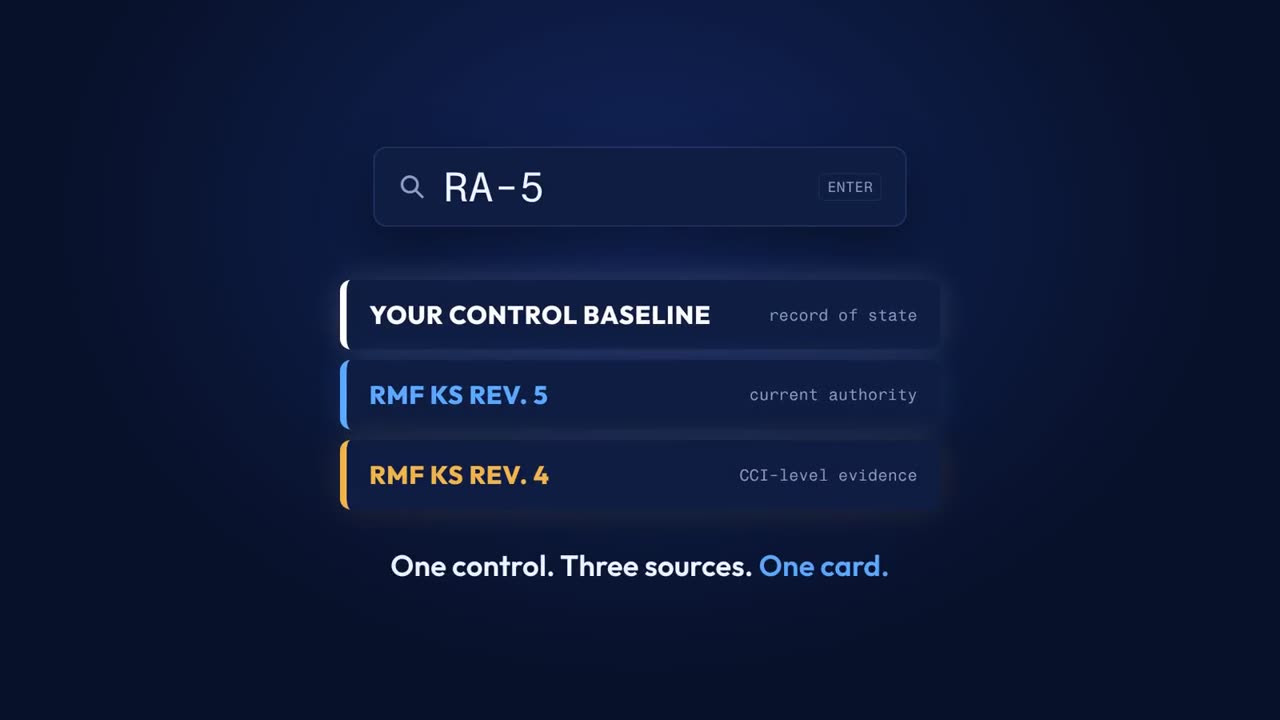
Built DRIFT to measure progress against the planned-control baseline, and the RMF KS Engine to put Rev. 4 evidence and Rev. 5 authority on one card per control.

Mission value

Every Monday, leadership sees what moved since last week and since the start, with the controls behind every number named.

Built for this programDRIFT RMF KS Engine

Featured program 03 · Operating model

Approved by leadership · three-track program underway

Service-Based Control Inheritance Model

Mission owner inheritance, rebuilt on evidence

Service design documents
11
Service design documents
Mission owner systems
13
Mission owner systems
Program tracks
3
Program tracks

Program leadership

Took the draft model to leadership, which approved it and stood it up as a formal program: refresh the service documents, align them to the model, then refresh the agreements mission owners sign.

Technical execution

Traced each control mission owners may inherit to the service that provides it. A control maps only when the source text names it, cited by statement ID and verbatim quote.

Mission value

Replaced an inherited-control list that could not be substantiated with one where every mapping is traceable and gaps are published instead of inferred.

Featured program 04 · Process design

Quarterly and weekly processes in operation

Continuous Validation and Repeatable Operations

From batch assessment to a steady operating rhythm

Hardware validation
Quarterly
Hardware validation
Leadership briefings
Weekly
Leadership briefings

Program leadership

Proposed an incremental validation model to the branch director, and advise program leadership on staffing and resources.

Technical execution

Established a quarterly hardware validation process between the authorization team and the hardware audit and CMDB team, backed by baseline drift analysis in the PPSM console.

Mission value

Designed to replace batch assessments whose results age during months-long reviews, while leadership gets a weekly view of the environment.

Built for this programPPSM Delta Analysis Console

Earlier programs

2023 – 2025

NASA HALO

Northrop Grumman

Led the RMF program for mission systems spanning ground, satellite communications and embedded hardware.

2024Innovation Award

2020 – 2022

Fortune 100 clients

PwC

Built a client risk dashboard that reduced compliance findings by 38%, and performed SOC 2 control assessments.

38%Fewer compliance findings

2015 – 2020

U.S. Navy, NAVWAR

Booz Allen Hamilton

Navy Qualified Validator for classified and tactical systems. Reached a 90-day authorization milestone and helped deliver PKI across 200+ ships.

200+Ships reached by PKI

03How I lead

Principles, shown in the work.

One cadence for every stakeholder.

A weekly governance rhythm keeps engineering, operations, assessors and authorizing officials on the same milestones. The Monday report says what moved, what regressed and which controls are behind each number.

See it in DRIFT

Every claim traces to a source.

Risk scores are checked against the matrix that governs them before an authorizing official reads them. Inheritance mappings cite the statement and the quote. If it cannot be traced, it is marked as a gap.

See it in RARE

Design for the person doing the work.

A Monday wizard for a Monday report. A marking selector and user guide so a tool can run on government equipment. No program names in a tool other teams will adopt.

See it in RMF KS Engine

Fix the constraint, not the symptom.

A 30 MB upload cap became a byte-budget splitter instead of a rescan. Assessment results that went stale during review became a proposal for continuous validation.

See it in Nessus Splitter

04Engineering and innovation

When the program hits a bottleneck, I build the way through.

My expertise spans cybersecurity governance, the DoD Risk Management Framework, NIST SP 800-53 and security authorization. I pair it with hands-on engineering and automation to solve problems that program management alone cannot.

PARALLAX

Program challenge
An authorization package changes every week.
Leadership decision
Chose a single offline file over a hosted application, giving up shared state in exchange for use on controlled data with no infrastructure.
Engineering solution
See exactly what moved between two versions of a security package.
Operational impact
A reviewer sees changed, removed and added controls in seconds, then drills into the exact field that moved and its before and after values.
Read the case study

Full portfolio

Films show real tools running on synthetic sample data

05Career and credentials

Fifteen years inside the authorization process.

I started in 2010 assessing classified systems for the Army and DHS, and spent the next decade on the inside of the authorization process: validating Navy tactical systems, leading programs for Fortune 100 clients and financial institutions, and running the RMF program for NASA’s HALO mission.

Along the way the work changed from checking controls to leading the programs around them. Today that means owning three authorization programs end to end, coordinating the people who implement, assess and approve them, and turning the result into something a decision maker can act on in one read.

The tools on this site came from that work. Each began as a bottleneck my team accepted as part of the job. I treat AI the same way I treat any capability on a mission network: useful when a person stays accountable for the output and the data stays where it belongs.

Certifications

  • PMP
  • CISM
  • CompTIA Security+
  • CompTIA Network+
  • CompTIA A+

Training I lead

  • Incident response tabletop exercises
  • NIST cybersecurity policy training
  • STIG Viewer manual assessment training
  • AI output guidance for a contractor workforce

B.S., Project Management & Information Systems

  1. 2025 – Now

    Peraton

    Senior Advisor, IA & Cybersecurity

    U.S. Marine Corps, MARFORCYBER / MCCOG. Lead the security authorization program for an operational hybrid cloud data center.

  2. 2023 – 2025

    Northrop Grumman

    Sr. Principal Cyber Systems Engineer

    NASA HALO. Led the RMF program for mission systems spanning ground, satellite communications and embedded hardware.

  3. 2022 – 2023

    Kaufman Rossin

    Cybersecurity Manager

    Led risk assessment and audit programs for financial institutions, including SOC 2, GLBA, FFIEC and ISO 27001.

  4. 2020 – 2022

    PwC

    Cybersecurity Manager, Strategy & Transformation

    Fortune 100 clients. Built a risk dashboard that reduced client compliance findings by 38%. Performed SOC 2 control assessments.

  5. 2015 – 2020

    Booz Allen Hamilton

    Lead Associate, Cybersecurity

    U.S. Navy, NAVWAR. Navy Qualified Validator for classified and tactical systems. Reached a 90-day authorization milestone and delivered PKI across 200+ ships.

  6. 2010 – 2015

    GDIT

    Sr. Cybersecurity Analyst

    U.S. Army and DHS. Assessment and authorization for classified systems. Led incident response tabletop exercises.

Recognition

  • 2025Peraton Gold Award · RMF automation across 1,400+ operational assets
  • 2024Northrop Grumman Innovation Award · RMF integration for NASA HALO
  • 2021PwC Consulting Excellence Award · Client risk dashboard
  • 2017, 2019Booz Allen Champion’s Heart Award · Navy authorizations and NAVWAR PKI enablement

Contact

Have a complex program that needs to ship? Let’s talk.

Open to Senior Technical Program Manager roles leading security, compliance and infrastructure programs. Based in the Washington, DC area.

Email

d.torres.resume@gmail.com

Email me

LinkedIn

linkedin.com/in/daniel-torres-cism

Open profile

Resume

Tailored to your role on request.

Request resume